Governance That Stays Inside Your Boundary
Run the cajeX data plane in your own cloud account for full data residency control. The same platform, deployed where your regulations require.
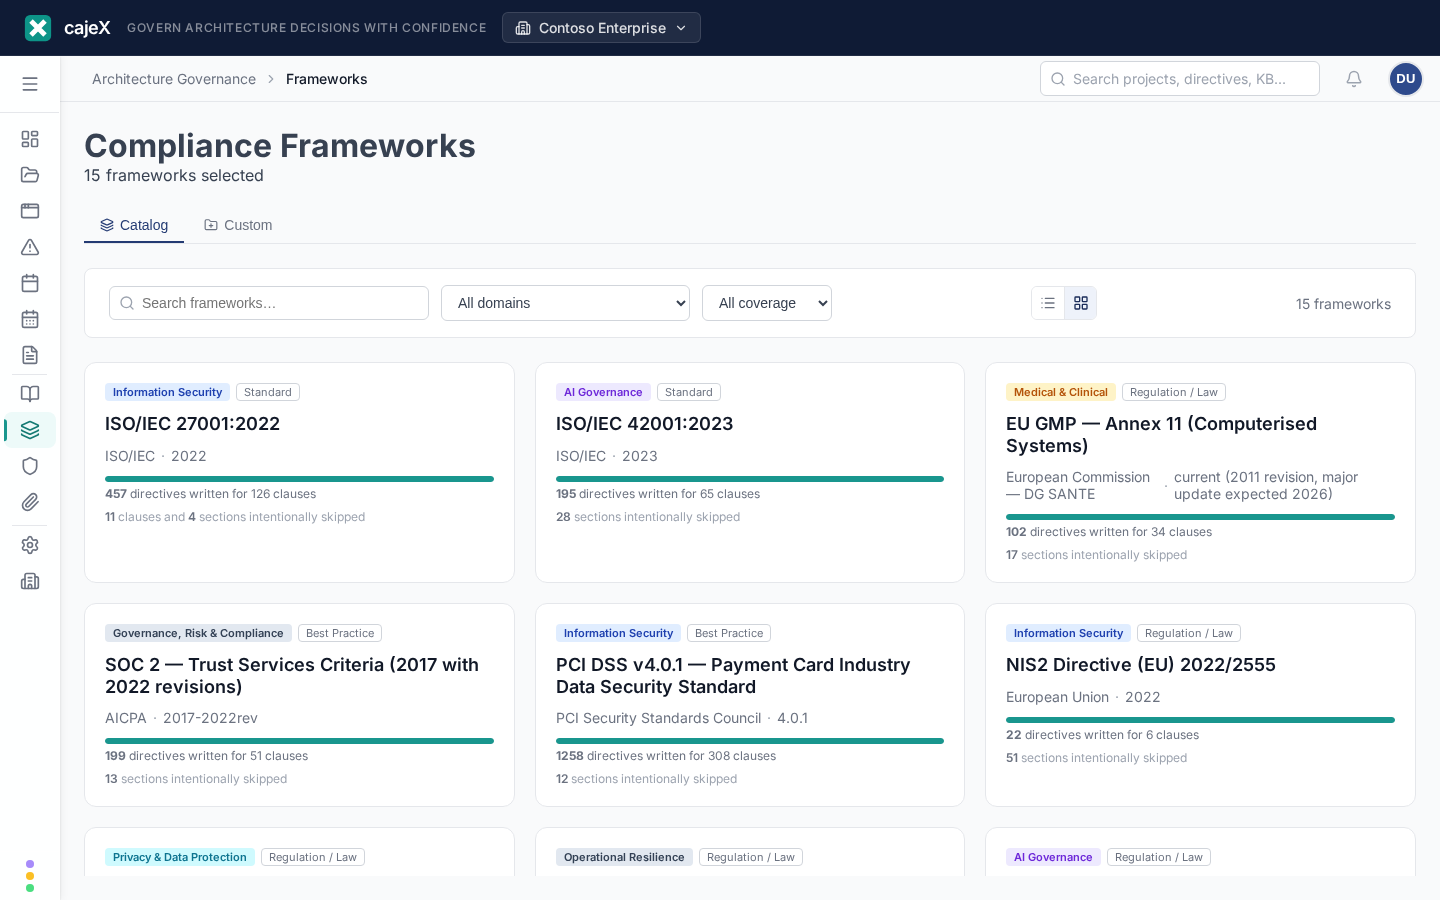
The Regulations You Answer To, as Directives
The framework catalogue already holds the rules regulated teams work under: 21 CFR Part 11, GAMP 5, EU GMP Annex 11 and Annex 15, the EU Falsified Medicines Directive and Good Distribution Practice, DORA, NIS2, and several hundred more. Each is broken down clause by clause into directives your architects approve, and every finding carries the clause it is about.
- Pharma and medical: 21 CFR Part 11, GAMP 5, EU GMP, EU FMD, EU GDP, IEC 62304
- Financial and operational resilience: DORA, NIS2, and national regimes
- Regulator-facing clauses shown and marked out of scope, with the reason
- A Framework Compliance report per project, built from live findings
From Requirement to Test Evidence
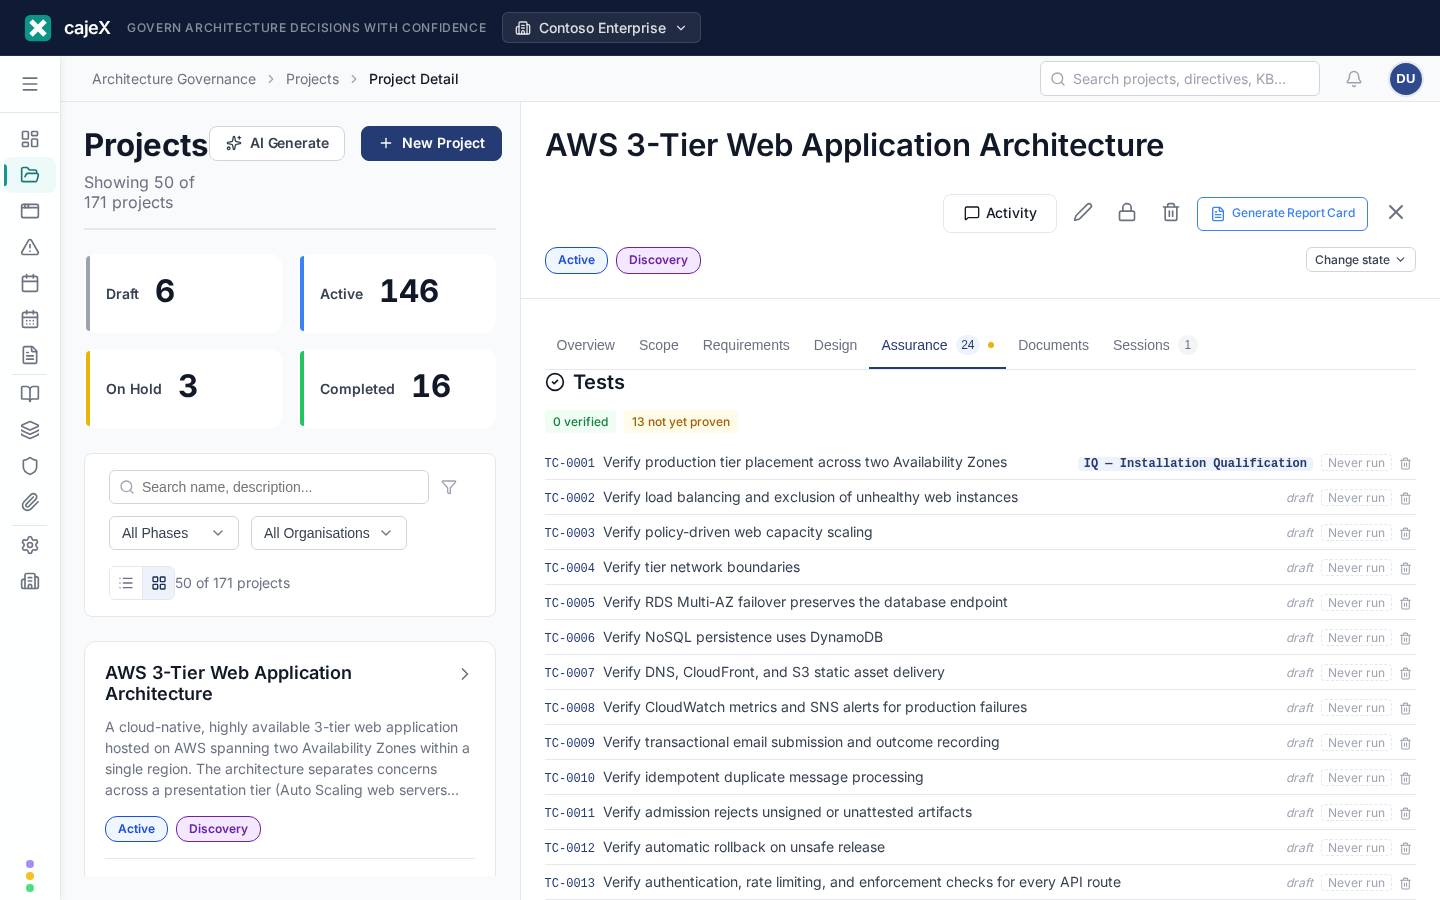
For a validated system, trace each requirement to the directive that forced it, compare suppliers' designs against the set, and record the tests that prove it. AI drafts IQ, OQ, and PQ protocols against the selected design for you to review; the vocabulary is yours to set. Turned on in Settings → Features.
- Requirements that derive from a directive are marked non-negotiable for suppliers
- Unmet must-haves open findings when a design is selected
- "Verified" only when every linked test has passed
- A protocol pack to hand to the supplier; not a validation execution system
Data Residency by Construction
Bring-Your-Own-Cloud: deploy the cajeX data plane inside your own AWS, Azure, GCP, or on-prem environment. The portable runtime ships as a Docker image paired with S3-compatible object storage (AWS S3, MinIO, or any compatible provider), so it runs wherever you can run a container. Your project data, findings, directives, documents, and audit logs never leave the environment you choose. The only outbound call from the data plane is an optional AI review API — which you can disable entirely if your data residency policy prohibits external processing.
- Bring-Your-Own-Cloud: run the data plane in your AWS, Azure, GCP, or on-prem environment
- Portable runtime ships as a Docker image with S3-compatible storage (AWS S3, MinIO, and compatible)
- Runs in any region and any account you control
- AI review features can be disabled to keep all data local
Control Plane / Data Plane Split
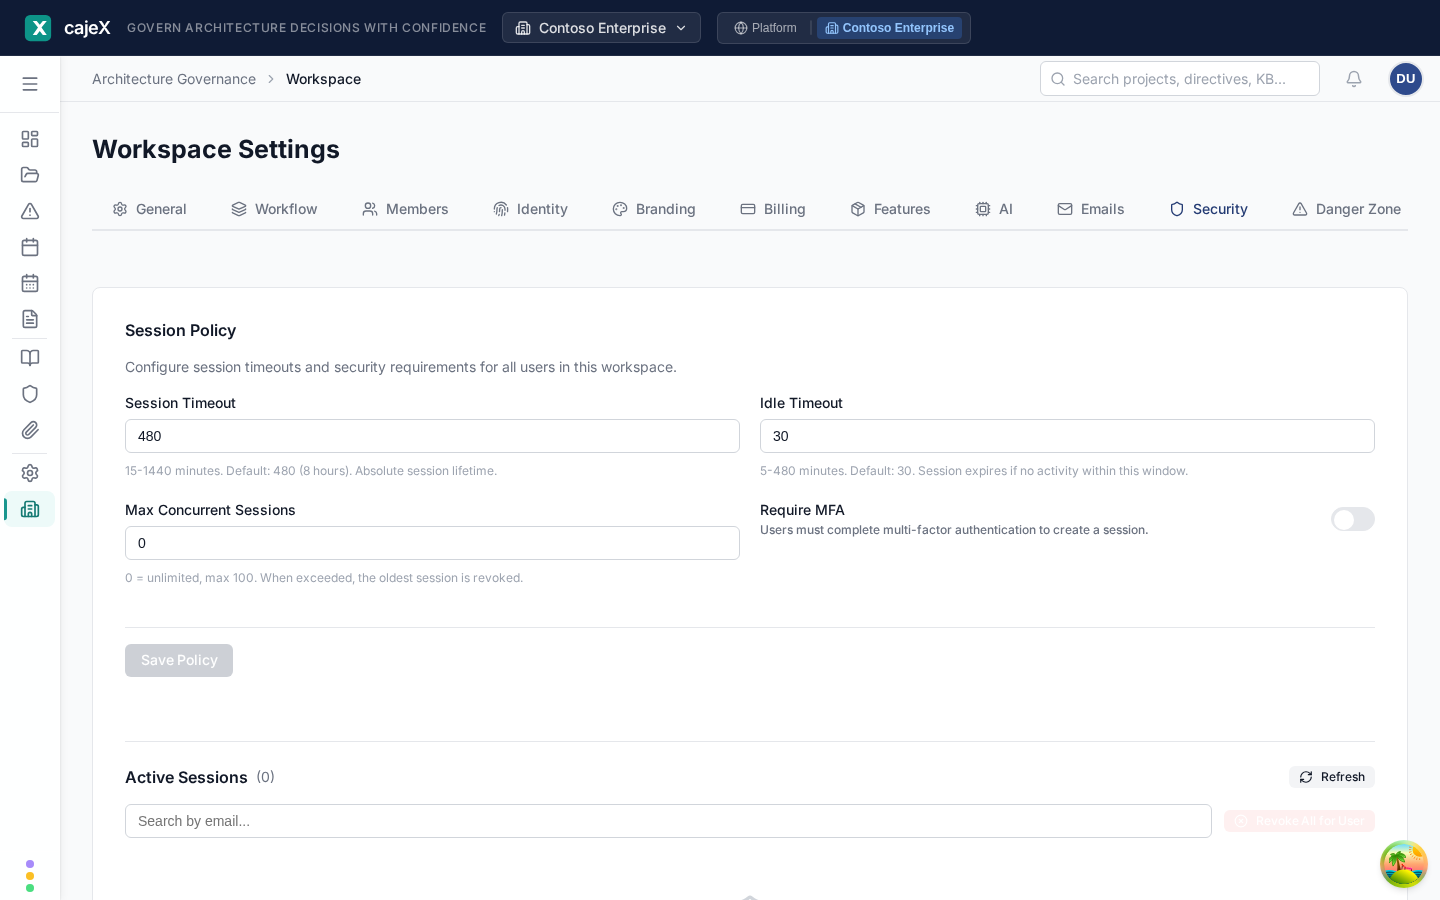
The control plane (identity, billing, platform admin) runs on Cloudflare. The data plane — everything that touches customer architecture data — runs inside your boundary. One codebase, two deployment targets. The private data plane is in development with design partners.
- Customer data handled exclusively by the data plane in your cloud
- JWT-based auth; control plane never sees project content
- In development with design partners — contact us before you plan around it
- Per-workspace or per-customer data planes supported
Immutable Audit Trails
Every review decision, comment, status change, and approval is recorded with immutable timestamps and user attribution. Export a complete chain of custody for auditors instead of assembling evidence from email threads and meeting notes.
- Immutable event log for every governance action
- User attribution with SSO identity verification
- GDPR-aligned data export and right-to-erasure workflows
- Scoped to your data plane — logs stay in your boundary
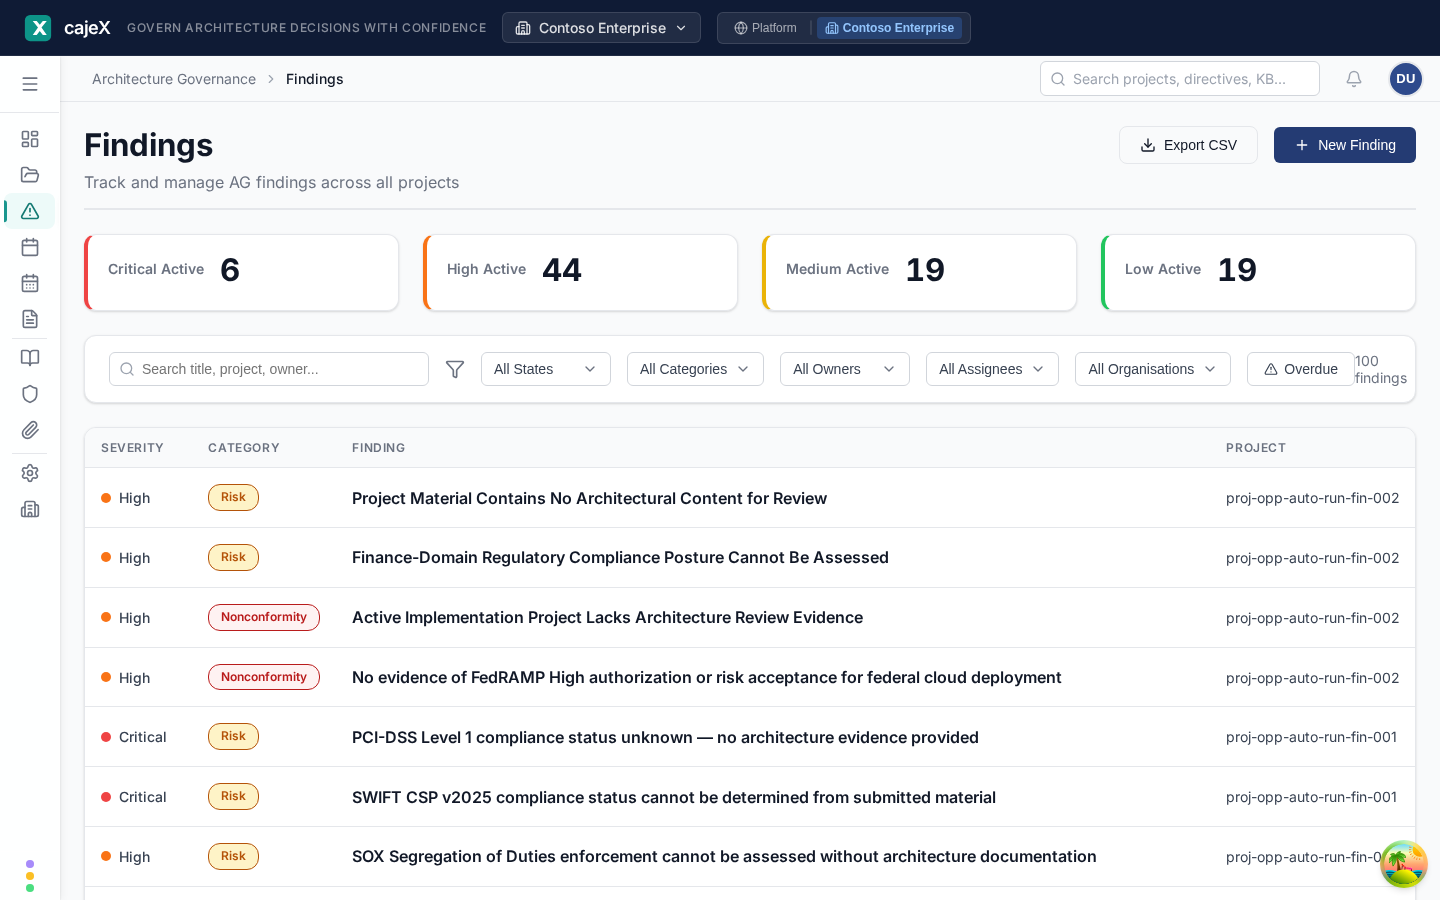
Workspace Isolation & Access Control
Complete data isolation: every record is keyed to its workspace, enforced by workspace-aware middleware on every API request — not just row-level filters. Role-based access control, enterprise SSO via OIDC and SAML, and SCIM provisioning keep access tight enough for regulated environments.
- Every record keyed to its workspace
- Middleware-enforced isolation on every API request
- Enterprise SSO via OIDC and SAML — native Entra ID integration plus generic OIDC for Okta and other providers
- SCIM 2.0 for automated user lifecycle management

Bring cajeX Inside Your Boundary
Talk to us about deploying the data plane into your AWS, Azure, GCP, or Kubernetes environment.