Architecture Governance That Auditors Love
Complete audit trails, automated compliance tracking, and evidence-ready exports — built into every review workflow.
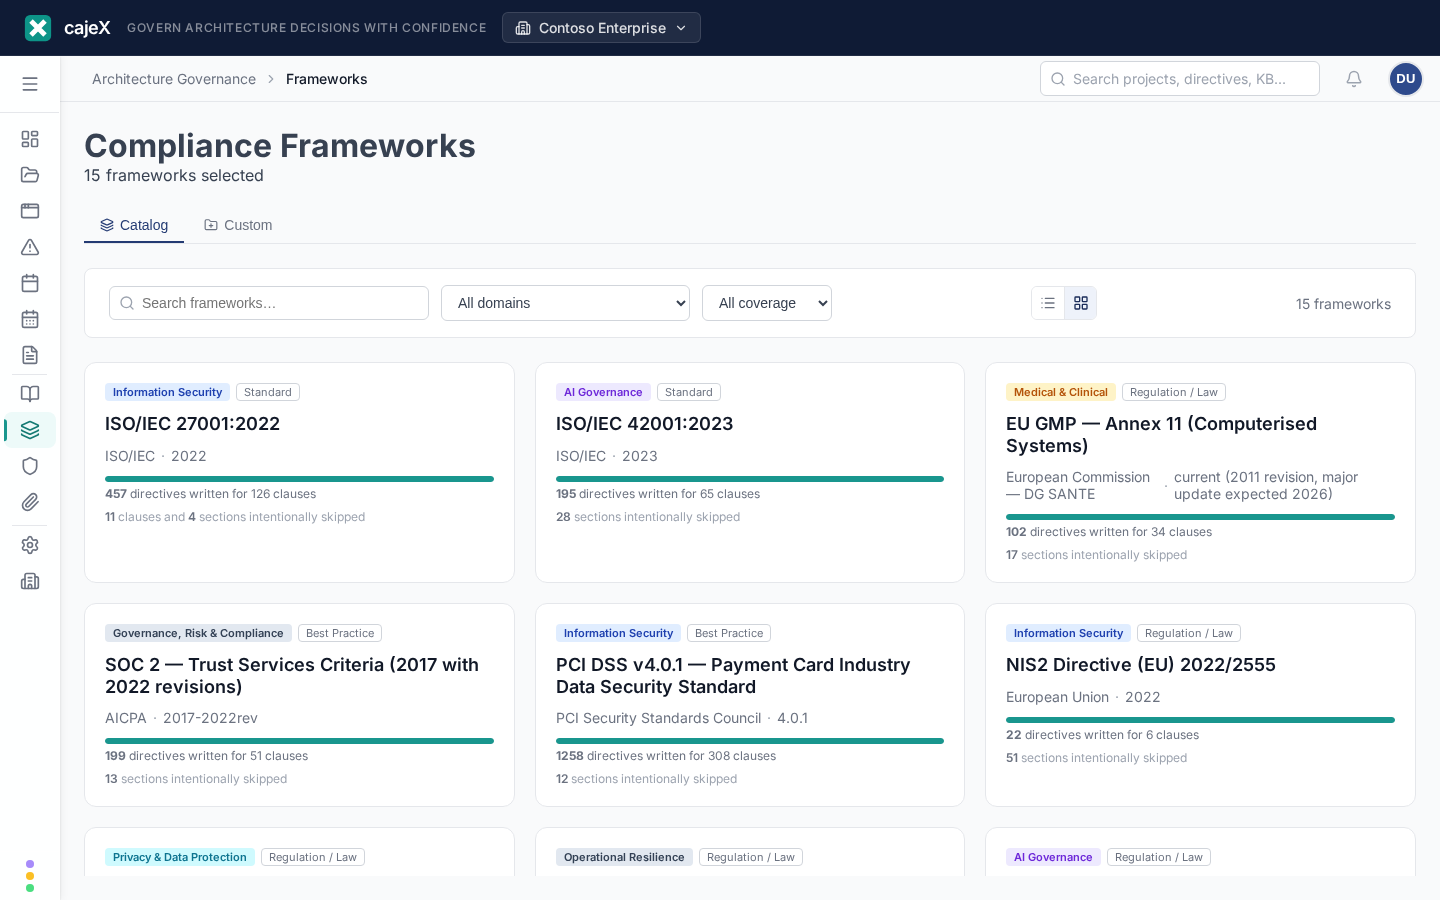
300+ Frameworks, Ready to Review Against
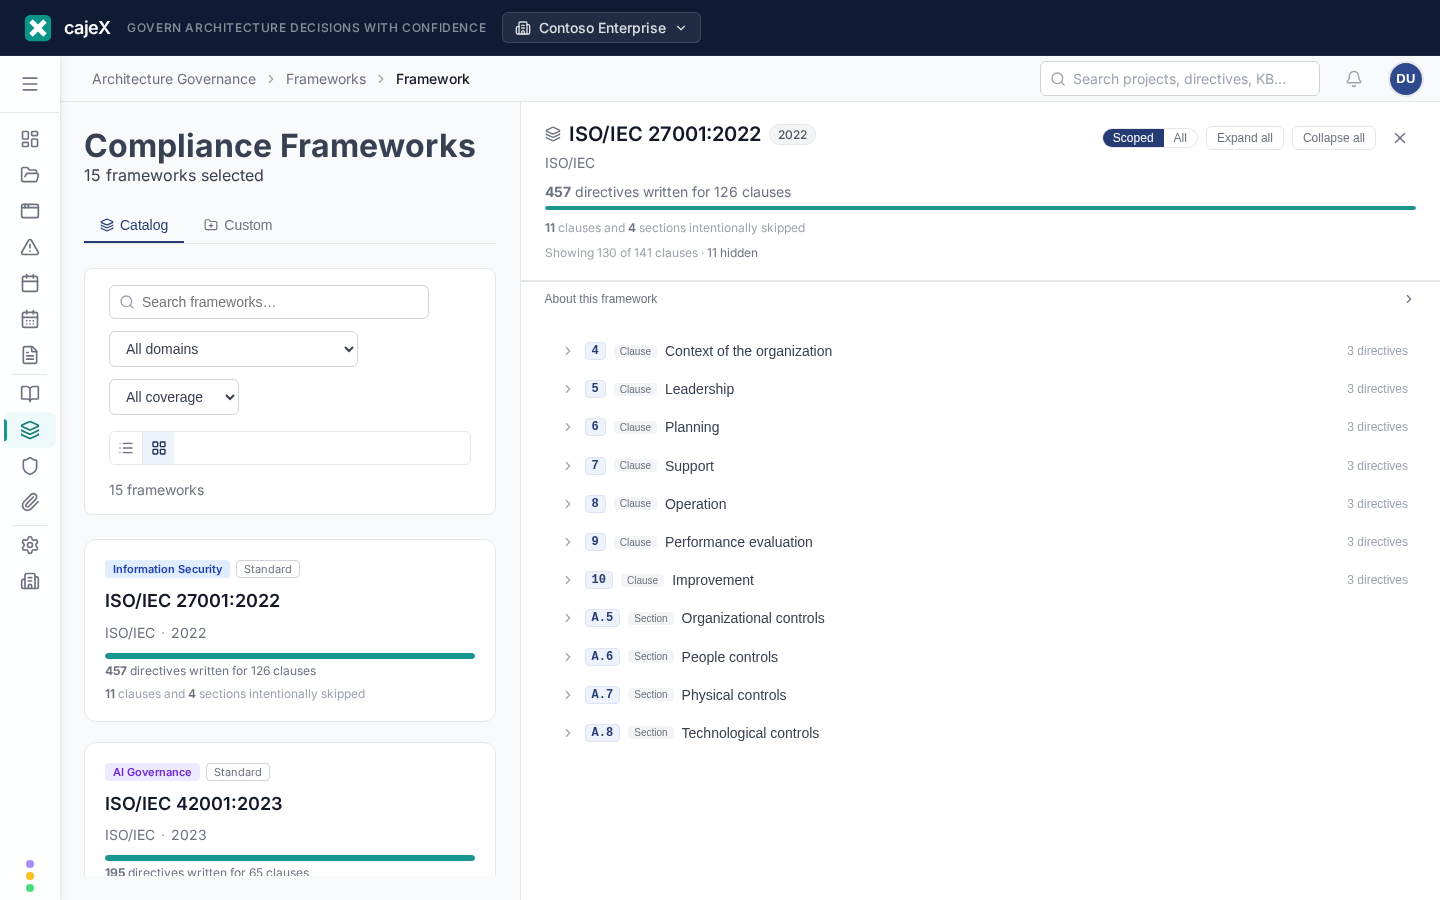
ISO 27001, NIST CSF 2.0, SOC 2, GDPR, the EU AI Act, DORA, NIS2, and several hundred more are already in the catalogue, each broken down into directives. Enable the ones that apply, approve the directives, and one project review produces evidence for every framework it touches.
- Recommendations from your industry during setup
- Clause-by-clause mapping your architects adopt, reword, or replace
- One review, evidence for every enabled framework
- Custom frameworks for internal audit packs on Enterprise plans
Immutable Audit Trails
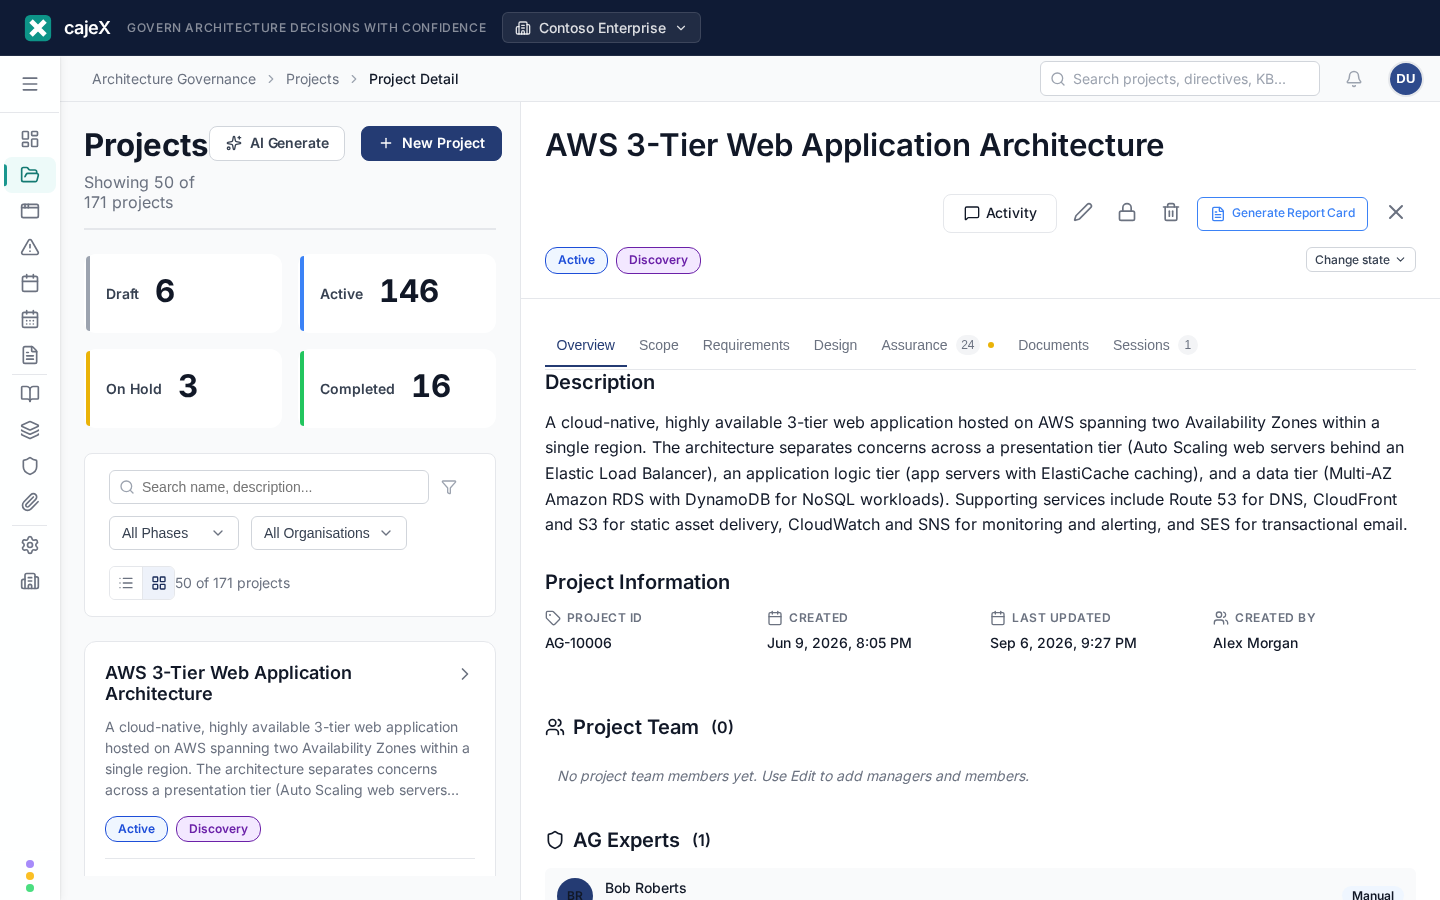
Every review decision, comment, status change, and approval is recorded with immutable timestamps and user attribution. When auditors request evidence, you export a complete chain of custody — not a patchwork of emails and meeting notes.
- Immutable event log for every governance action
- User attribution with SSO identity verification
- One-click export for external audit teams
GDPR-Compliant Data Handling
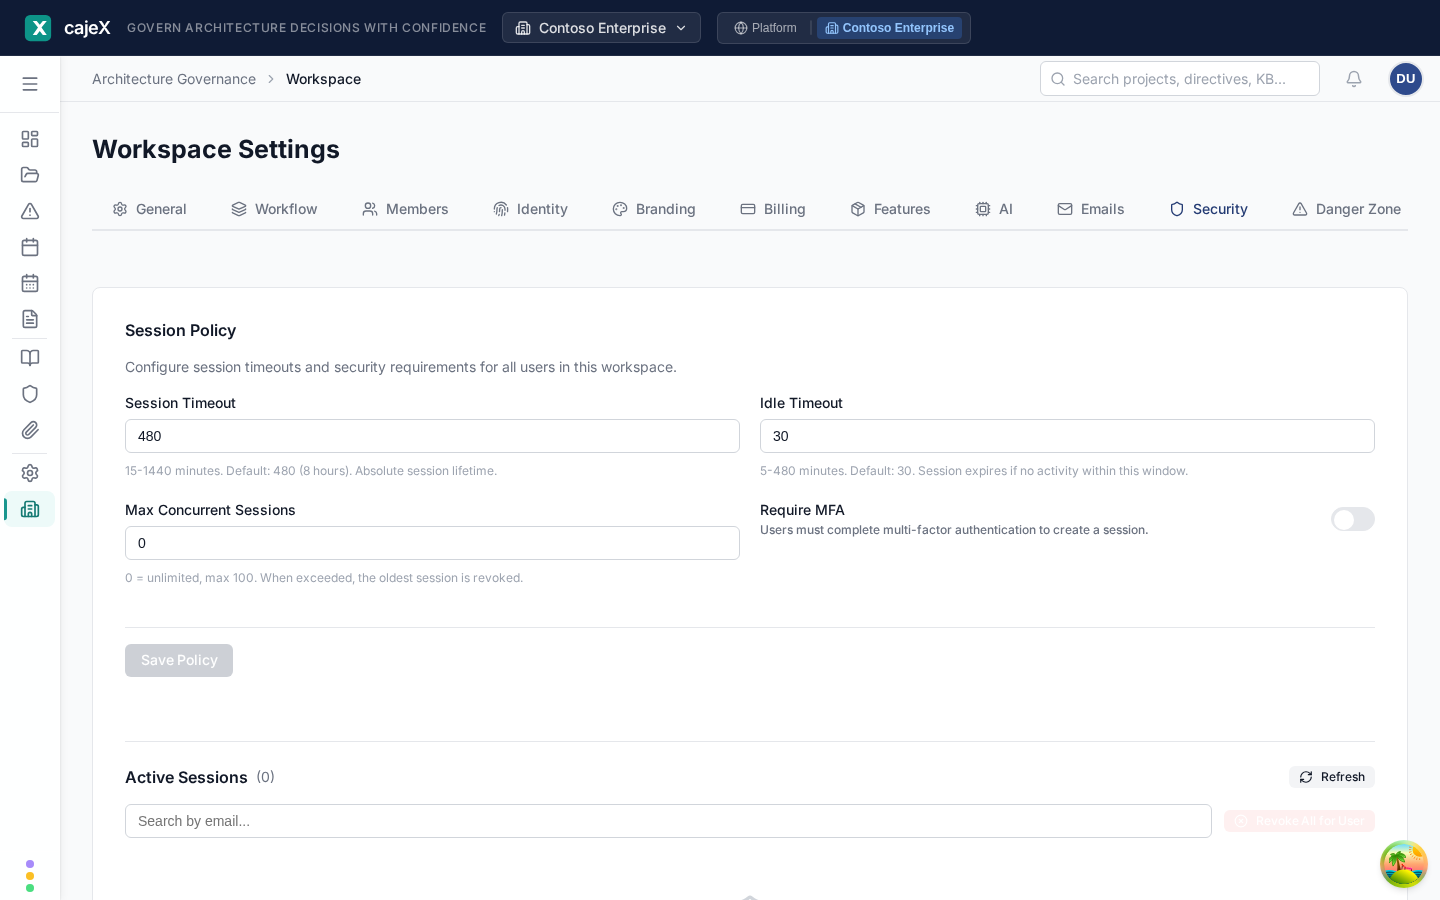
cajeX is built with data protection by design. Export everything your workspace holds in an open format, delete a workspace with a 30-day recovery window before it is purged, and control sessions and sign-in policy per workspace. A Data Processing Agreement is available to every customer.
- Workspace export in an open format, with a manifest
- Workspace deletion with a 30-day recovery window, then purge
- Session policy and MFA requirement per workspace
Automated Finding Tracking
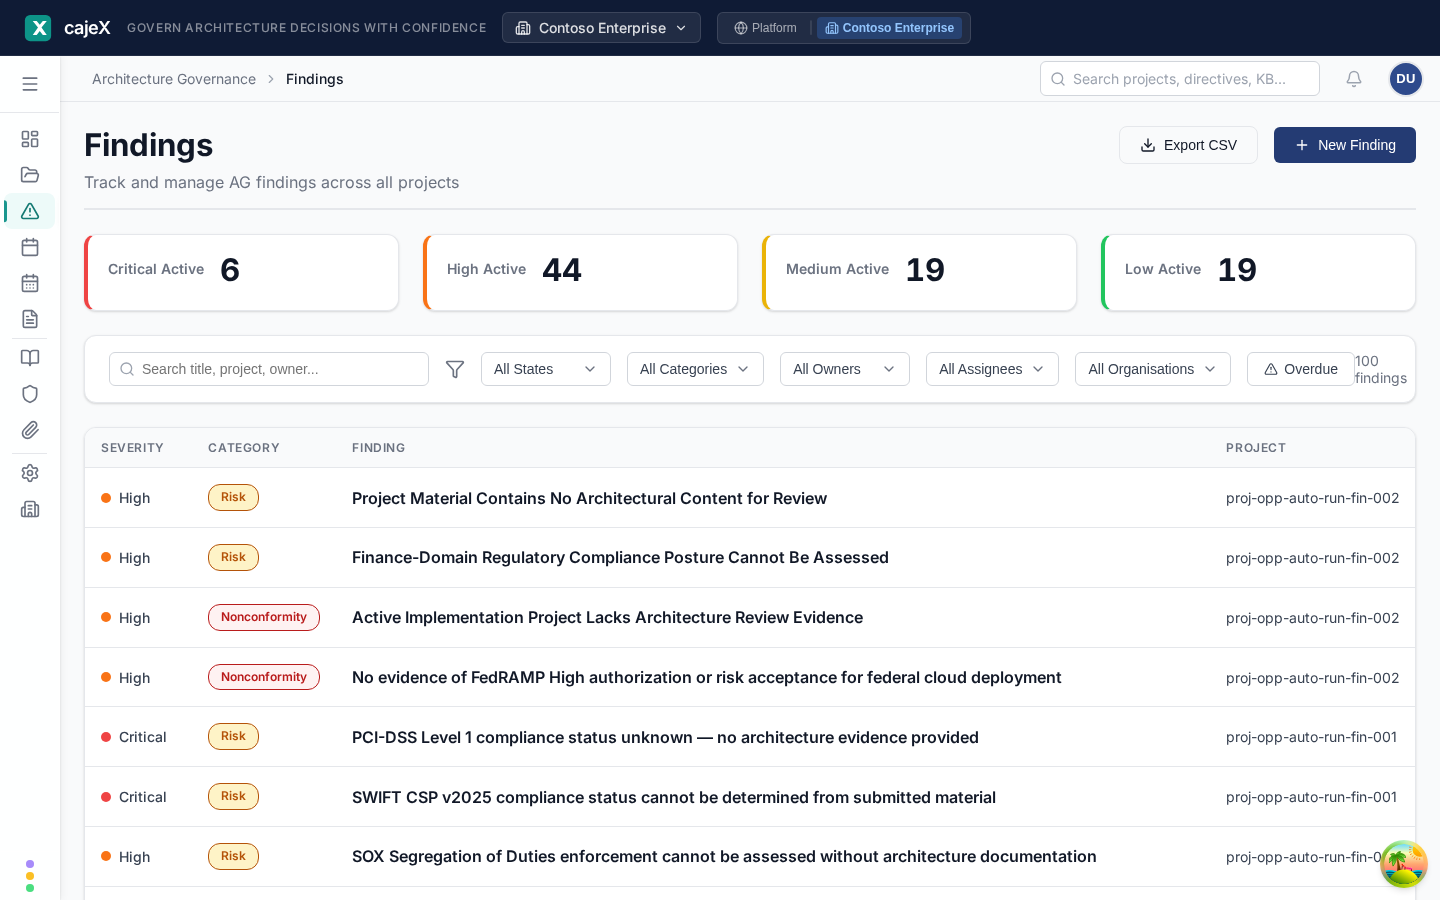
AI-generated findings link directly to the directive they violate. Each finding has a severity, a recommended remediation, and an owner. Nothing slips through the cracks because every finding has an owner and a due date, and stays open until someone closes, defers, or rejects it on the record.
- Findings linked to specific architecture directives
- Severity classification: Critical, High, Medium, Low
- Owner, due date, and a readable state-change history on every finding
Framework Conformance
Enable the frameworks you answer to from a catalogue of more than 300, and every finding carries its trail: framework, clause, directive. The dashboard shows conformance by directive and which directives collect the most open findings — so governance stops being a black box and starts being something you can prove.
- Framework → clause → directive → finding, on every finding
- Framework Compliance report, readable on screen
- Overdue findings flagged on the dashboard and by email
Pass Your Next Audit With Confidence
See how cajeX generates the evidence your compliance team needs — automatically.