300+ Frameworks, Already Turned Into Directives
Regulations, standards and engineering practices, each broken down clause by clause into directives you can approve, review against and report on.
The Blank-Page Problem
Every architecture team knows it has to turn its obligations into rules a design can be checked against. Few have the time to read a regulation clause by clause and write those rules, and most governance programmes stall before the library is finished.
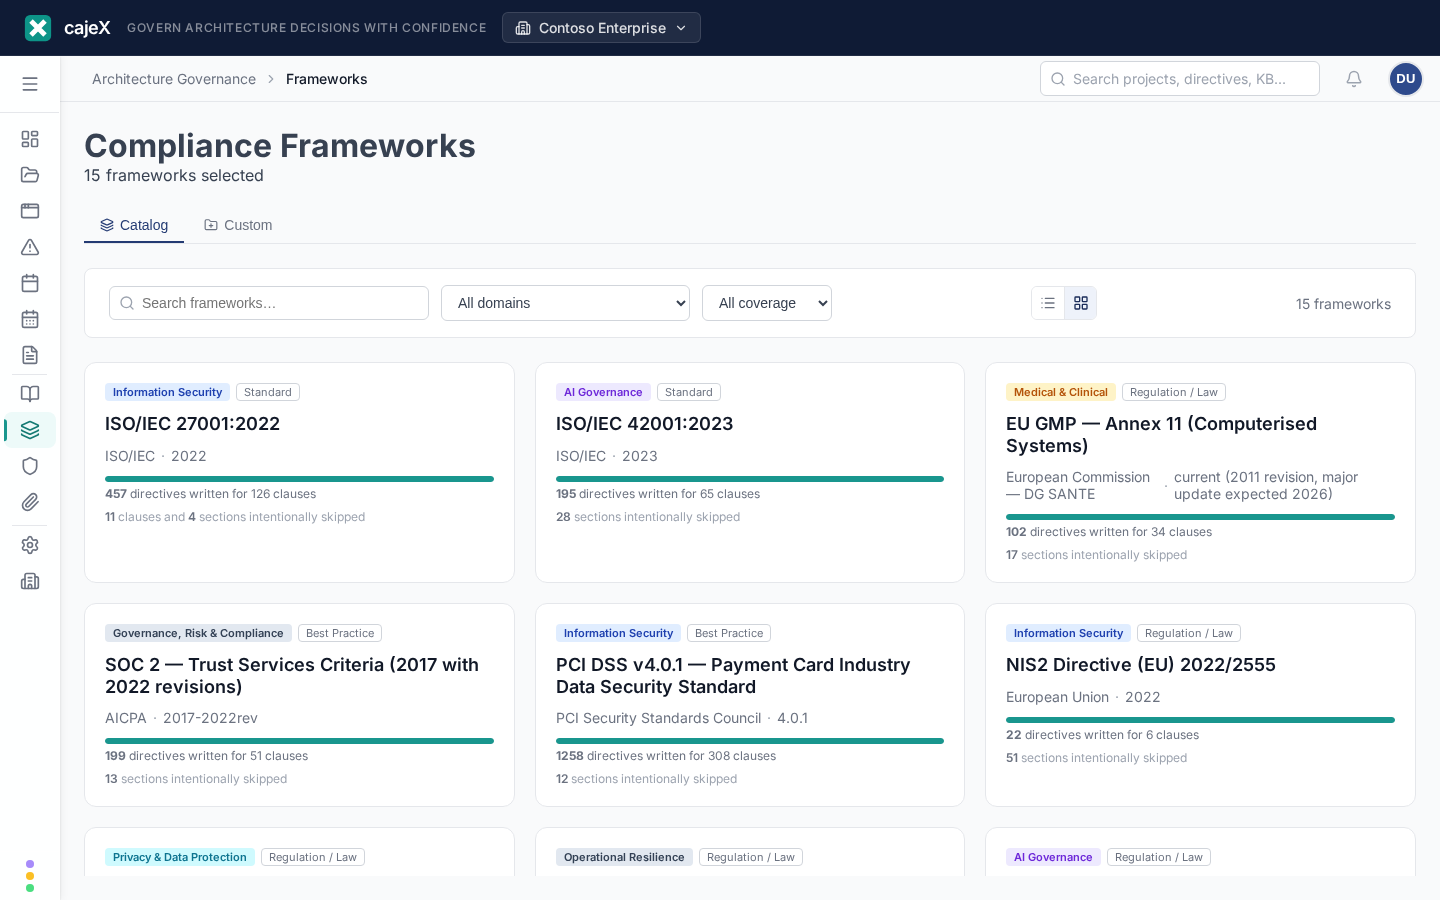
The framework catalogue removes the blank page. Each framework has already been read and broken down. Every clause is treated as a question your organisation has to answer, and cajeX suggests the directive that answers it. Your architects decide what to adopt.
From there, frameworks behave like the rest of cajeX. Directives are approved, projects are reviewed against them, and findings show where you conform and where you do not, each one traceable to the clause it is about.
From Obligation to Evidence
Four steps from choosing a framework to a finding you can show an auditor.
Choose
Pick the frameworks you answer to. cajeX recommends some from your industry during setup.
Review the mapping
Each clause is a question. cajeX suggests the directive that answers it.
Approve
Adopt a directive as written, reword it, or write your own. The decision stays with your architects.
Review and report
Every project is reviewed against the approved set, and every finding carries its clause.
What You Can Do With a Framework
A framework in cajeX is not a checklist. It is a set of rules your reviews and reports run on.
Recommended for you
During setup, cajeX recommends frameworks from your industry and says what each applies to. You choose; nothing is switched on for you.
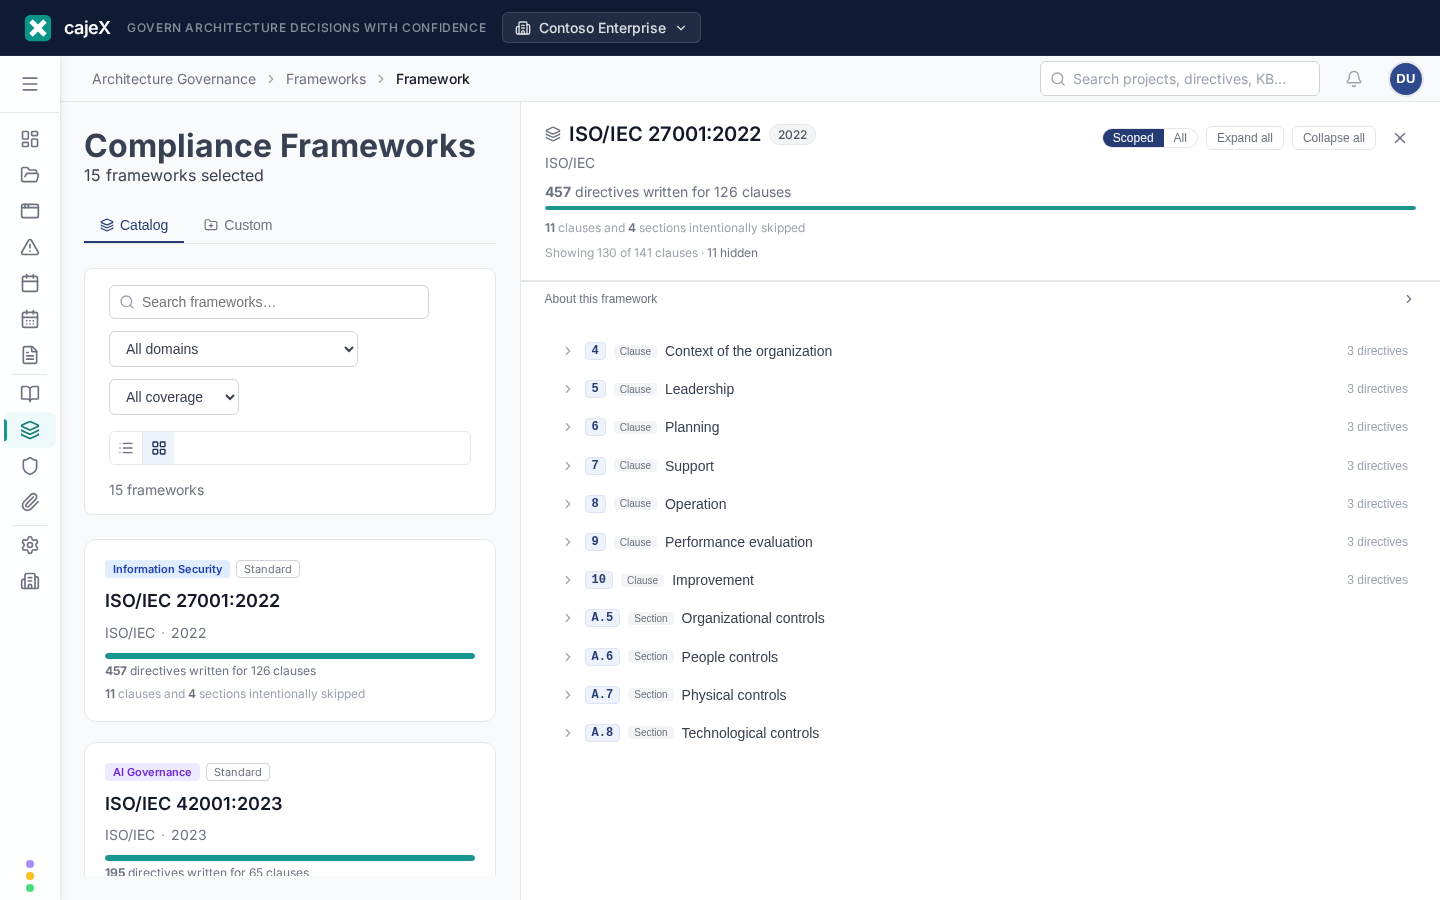
Browse by framework or by domain
Open a framework and walk its clauses, or browse your directives grouped by the framework they came from. Clauses addressed to regulators rather than to you are shown and marked out of scope, with the reason.
A trail on every finding
A finding raised against a framework directive shows the whole path: framework, clause, directive. An auditor can follow it in either direction.
Framework Compliance report
A readable, on-screen report of where a project stands against a framework, clause by clause, built from the same findings your team works on.
Reviews scoped to a framework
Run an AI review against one framework or a whole domain instead of every approved directive, so a review answers the question you are actually asking.
Honest about the source
Where a publisher allows it, clause text is quoted. Where the publisher keeps the copyright, cajeX summarises the clause and labels the framework as summarised, with attribution.
Which frameworks apply to this application?
With Applications turned on, each application shows the frameworks that apply to it, worked out from its data classification and criticality, with the reason for every match. Frameworks that did not match are still listed, so nothing is hidden. cajeX recommends and explains; you decide.
Your own frameworks
On Enterprise and Private Cloud plans, group your own directives into named custom frameworks, separate from the catalogue: an internal audit pack, a customer's contractual obligations, a group security baseline. A workspace owner or admin turns this on in Settings → Features.
The Catalogue
307 frameworks in 20 domains. Open a domain to see what is in it. A workspace can enable 2 on Free, 7 on Basic, 15 on Pro, 31 on Team and unlimited on Enterprise.
Information Security52
- 3GPP TS 33.501 — 5G System Security Architecture and ProceduresStandard · 3GPP / ETSI
- APRA CPS 234 — Information SecurityRegulation · Australian Prudential Regulation Authority (APRA)
- ASD Essential Eight (Australian Signals Directorate / ACSC)Best practice · Australian Signals Directorate / ACSC
- BSI IT-GrundschutzBest practice · Bundesamt für Sicherheit in der Informationstechnik (BSI)
- China MLPS 2.0 — Multi-Level Protection Scheme (等保 2.0)Regulation · Ministry of Public Security (MPS), People's Republic of China
- CIS Controls v8 — Center for Internet Security Critical Security ControlsBest practice · Center for Internet Security
- CJIS Security Policy — Criminal Justice Information ServicesRegulation · FBI Criminal Justice Information Services
- CMMC 2.0 — Cybersecurity Maturity Model CertificationRegulation · US Department of Defense
- CRI Profile — Cyber Risk Institute Profile (Financial Sector)Best practice · Cyber Risk Institute (CRI)
- DO-326A / ED-202A + DO-356A / DO-355 / DO-379 — Airworthiness Security Process familyStandard · RTCA / EUROCAE
- ETSI EN 303 645 — Cyber Security for Consumer IoTStandard · ETSI (European Telecommunications Standards Institute)
- FIRST CVSS — Common Vulnerability Scoring SystemBest practice · FIRST.org — Forum of Incident Response and Security Teams
- GLBA Safeguards Rule (16 CFR Part 314)Regulation · Federal Trade Commission
- GSMA Network Equipment Security Assurance Scheme (NESAS) / 3GPP SCASBest practice · GSMA + 3GPP
- HIPAA Security Rule (45 CFR Part 164 Subpart C)Regulation · US Department of Health and Human Services
- HITRUST CSF® — Common Security FrameworkBest practice · HITRUST Alliance
- HKMA C-RAF — Cyber Resilience Assessment FrameworkRegulation · Hong Kong Monetary Authority (HKMA)
- India RBI Cyber Security Framework + CERT-In DirectionsRegulation · Reserve Bank of India (RBI) / CERT-In
- IRS Publication 1075 — Tax Information Security GuidelinesRegulation · Internal Revenue Service
- ISO 27799:2016 — Health Informatics: Information Security Management in HealthStandard · ISO
- ISO/IEC 27001:2022Standard · ISO/IEC
- ISO/IEC 27002:2022Standard · ISO/IEC
- ISO/IEC 27032:2023 — Guidelines for Internet SecurityStandard · ISO/IEC
- ISO/IEC 27034 — Application SecurityStandard · ISO/IEC
- ISO/IEC 27400:2022 — IoT Security and Privacy GuidelinesStandard · ISO/IEC
- ITSG-33 — IT Security Risk Management (Canada)Best practice · Canadian Centre for Cyber Security (CCCS), Communications Security Establishment
- Japan METI Cybersecurity Management GuidelinesBest practice · Ministry of Economy, Trade and Industry (METI), Japan / IPA
- Korea ISMS-P — Information Security & Personal Information Management SystemRegulation · Korea Internet & Security Agency (KISA)
- MAS TRM — Technology Risk Management GuidelinesBest practice · Monetary Authority of Singapore (MAS)
- MITRE ATT&CK — Adversarial Tactics, Techniques, and Common Knowledge (Enterprise)Best practice · The MITRE Corporation
- MITRE D3FEND — Defensive Countermeasures Knowledge GraphBest practice · The MITRE Corporation
- MVSP — Minimum Viable Secure ProductBest practice · MVSP Working Group (mvsp.dev)
- NEN 7510 — Dutch Health Information SecurityStandard · NEN (Royal Netherlands Standardization Institute)
- NIS2 Directive (EU) 2022/2555Regulation · European Union
- NIST Cybersecurity Framework 2.0Best practice · NIST
- NIST IR 8259 / 8259A / 8425 — IoT Device CybersecurityBest practice · NIST
- NIST SP 800-171 Revision 3 — Protecting Controlled Unclassified Information in Nonfederal Systems and OrganizationsStandard · National Institute of Standards and Technology
- NIST SP 800-172 — Enhanced Security Requirements for Protecting CUIStandard · National Institute of Standards and Technology (NIST)
- NIST SP 800-53 Revision 5 — Security and Privacy Controls for Information Systems and OrganizationsStandard · National Institute of Standards and Technology
- NIST SP 800-61 — Computer Security Incident Handling GuideStandard · NIST
- NYDFS 23 NYCRR Part 500 — Cybersecurity RequirementsRegulation · New York Department of Financial Services
- OWASP API Security Top 10 (2023)Best practice · OWASP Foundation
- OWASP ASVS — Application Security Verification StandardBest practice · OWASP Foundation
- OWASP MASVS — Mobile Application Security Verification StandardBest practice · OWASP
- OWASP Proactive ControlsBest practice · OWASP
- OWASP Top 10 — Web Application Security RisksBest practice · OWASP
- PCI DSS v4.0.1 — Payment Card Industry Data Security StandardBest practice · PCI Security Standards Council
- STIX / TAXII — Threat Intelligence ExchangeStandard · OASIS Open
- SWIFT Customer Security Programme (CSCF)Best practice · SWIFT
- TISAX — Trusted Information Security Assessment Exchange (VDA ISA)Best practice · ENX Association (on behalf of VDA)
- UK Cyber Essentials (+ Cyber Essentials Plus)Best practice · NCSC / IASME
- UK NCSC Cyber Assessment Framework (CAF)Best practice · NCSC
Engineering Practices31
- Automotive SPICE (ASPICE) v4.0Best practice · VDA QMC (Verband der Automobilindustrie Quality Management Center)
- AWS Well-Architected — Cost Optimization PillarBest practice · Amazon Web Services (AWS)
- AWS Well-Architected — Operational Excellence PillarBest practice · Amazon Web Services (AWS)
- AWS Well-Architected — Performance Efficiency PillarBest practice · Amazon Web Services (AWS)
- Backstage Maturity ModelBest practice · Spotify (CNCF Incubating)
- cajeX General Best PracticesBest practice · cajeX
- CMMI for Development v3.0 — Capability Maturity Model IntegrationBest practice · ISACA (CMMI Institute)
- CNCF Cloud Native Maturity ModelBest practice · Cloud Native Computing Foundation (CNCF)
- DORA Capabilities Model (Google DORA)Best practice · Google Cloud / DORA (DevOps Research and Assessment)
- Google Cloud Architecture Framework — Cost Optimization PillarBest practice · Google LLC
- Google Cloud Architecture Framework — Operational Excellence PillarBest practice · Google LLC
- Google Cloud Architecture Framework — Performance Optimization PillarBest practice · Google LLC
- Google Site Reliability Engineering (SRE)Best practice · Google
- Google Testing PracticesBest practice · Google LLC (Google Testing Blog + Software Engineering at Google)
- ISO/IEC 20000-1 — Service Management SystemStandard · ISO/IEC
- ISO/IEC 25010 — Software Quality ModelStandard · ISO/IEC
- ISO/IEC/IEEE 12207 + 15288 — Software & Systems Life Cycle ProcessesStandard · ISO/IEC/IEEE
- ISO/IEC/IEEE 29119 — Software TestingStandard · ISO/IEC/IEEE joint publication
- ISTQB — Foundation Level SyllabusBest practice · International Software Testing Qualifications Board (ISTQB®)
- IT4IT® — IT Operating Model Reference ArchitectureBest practice · The Open Group
- ITIL 4 — IT Infrastructure Library (Service Management)Best practice · PeopleCert (formerly AXELOS)
- Microsoft Azure Well-Architected — Cost Optimization PillarBest practice · Microsoft Corporation
- Microsoft Azure Well-Architected — Operational Excellence PillarBest practice · Microsoft Corporation
- Microsoft Azure Well-Architected — Performance Efficiency PillarBest practice · Microsoft Corporation
- OWASP DSOMM — DevSecOps Maturity ModelBest practice · OWASP
- PMBOK Guide — Seventh Edition (PMI)Best practice · Project Management Institute
- PRINCE2 7e — PRojects IN Controlled EnvironmentsBest practice · PeopleCert
- SAFe 6.0 — Scaled Agile FrameworkBest practice · Scaled Agile, Inc.
- The Twelve-Factor AppBest practice · Adam Wiggins / Heroku (open methodology)
- TMMi — Test Maturity Model IntegratedBest practice · TMMi Foundation
- xUnit Test Patterns: Refactoring Test Code (Meszaros 2007)Best practice · Gerard Meszaros (Addison-Wesley)
Privacy & Data Protection25
- Australia Privacy Act 1988 + Australian Privacy Principles (APPs)Regulation · Australia (Office of the Australian Information Commissioner — OAIC)
- CCPA/CPRA — California Consumer Privacy Act + California Privacy Rights ActRegulation · State of California
- China PIPL — Personal Information Protection LawRegulation · People's Republic of China (Cyberspace Administration of China — CAC)
- Colorado Privacy Act (CPA)Regulation · State of Colorado (Attorney General)
- Connecticut Data Privacy Act (CTDPA)Regulation · State of Connecticut
- COPPA — Children's Online Privacy Protection Act + RuleRegulation · U.S. Federal Trade Commission (FTC)
- FERPA — Family Educational Rights and Privacy ActRegulation · US Department of Education
- General Data Protection Regulation (EU 2016/679)Regulation · European Union
- HIPAA Privacy Rule (45 CFR Part 164 Subpart E)Regulation · US Department of Health and Human Services
- India DPDP Act 2023 — Digital Personal Data Protection ActRegulation · Government of India (Ministry of Electronics and IT)
- ISO 31700 — Privacy by Design for Consumer Goods and ServicesStandard · ISO
- ISO/IEC 27018:2019 — Code of Practice for Protection of PII in Public Clouds Acting as PII ProcessorsStandard · ISO
- ISO/IEC 27701:2025 — Privacy Information Management System (PIMS)Standard · ISO/IEC
- Japan APPI — Act on the Protection of Personal InformationRegulation · Japan (Personal Information Protection Commission — PPC)
- LGPD — Lei Geral de Proteção de Dados (Brazil)Regulation · Brazil (ANPD — Autoridade Nacional de Proteção de Dados)
- NIST Privacy Framework 1.0Best practice · NIST
- PIPEDA — Personal Information Protection and Electronic Documents Act (Canada)Regulation · Government of Canada (Office of the Privacy Commissioner)
- POPIA — Protection of Personal Information Act (South Africa)Regulation · South Africa (Information Regulator)
- Quebec Law 25 (Bill 64) — Protection of Personal InformationRegulation · Government of Quebec / Commission d'accès à l'information (CAI)
- Saudi Arabia PDPL — Personal Data Protection LawRegulation · SDAIA (Saudi Data and AI Authority)
- Singapore PDPA — Personal Data Protection ActRegulation · Government of Singapore / PDPC
- Switzerland nFADP — revised Federal Act on Data ProtectionRegulation · Swiss Confederation / FDPIC
- Texas Data Privacy and Security Act (TDPSA)Regulation · State of Texas
- UK GDPR + Data Protection Act 2018Regulation · UK Government / ICO
- Virginia Consumer Data Protection Act (VCDPA)Regulation · Commonwealth of Virginia
AI Governance24
- California AB 2013 — Generative AI: Training Data TransparencyRegulation · State of California
- California AB 3030 — Health Care Services: Artificial IntelligenceRegulation · State of California
- California SB 1120 — Physicians Made Decisions Act (Healthcare AI)Regulation · State of California
- CD4ML — Continuous Delivery for Machine LearningBest practice · ThoughtWorks / Martin Fowler
- Colorado Artificial Intelligence ActRegulation · State of Colorado
- EEOC Technical Assistance — AI in Employment Selection Under Title VIIBest practice · U.S. Equal Employment Opportunity Commission (EEOC)
- EU Artificial Intelligence Act (Regulation (EU) 2024/1689)Regulation · European Union
- Google Cloud MLOps Maturity ModelBest practice · Google Cloud
- IEEE 7000-2021 — Model Process for Addressing Ethical Concerns During System DesignStandard · IEEE
- ISO/IEC 23053 — Framework for AI Systems Using Machine LearningStandard · ISO/IEC
- ISO/IEC 23894:2023 — Information technology — Artificial intelligence — Guidance on risk managementStandard · ISO/IEC JTC 1/SC 42
- ISO/IEC 25059 — Quality Model for AI SystemsStandard · ISO/IEC
- ISO/IEC 42001:2023Standard · ISO/IEC
- ISO/IEC 42005 — AI System Impact AssessmentStandard · ISO/IEC
- ISO/IEC 5338 — AI System Life Cycle ProcessesStandard · ISO/IEC
- Microsoft MLOps Maturity ModelBest practice · Microsoft
- ML Test Score — Rubric for ML Production ReadinessBest practice · Google
- NAIC Model Bulletin — Use of AI Systems by InsurersRegulation · NAIC
- New York City Local Law 144 — AEDT Bias AuditRegulation · New York City Department of Consumer and Worker Protection (DCWP)
- NIST AI 600-1 — Generative AI ProfileBest practice · U.S. National Institute of Standards and Technology
- NIST AI Risk Management Framework 1.0Best practice · U.S. National Institute of Standards and Technology
- OECD AI PrinciplesBest practice · Organisation for Economic Co-operation and Development
- Singapore Model AI Governance Framework (+ Model GenAI Governance Framework)Best practice · IMDA / PDPC Singapore
- Texas Responsible AI Governance Act (HB 149)Regulation · State of Texas
OT/ICS Security19
- IACS UR E26 — Cyber Resilience of ShipsStandard · IACS
- IEC 62351 — Power System Communications SecurityStandard · IEC
- IEC 62443-3-3:2013 — System Security Requirements + Security LevelsStandard · International Electrotechnical Commission
- IMO Maritime Cyber Risk ManagementRegulation · IMO
- ISA/IEC 62443-1-1 — Terminology, Concepts and ModelsStandard · International Society of Automation / IEC
- ISA/IEC 62443-1-3 — System Security Compliance MetricsStandard · International Society of Automation / IEC
- ISA/IEC 62443-2-1 — Security Program Requirements for IACS Asset OwnersStandard · International Society of Automation / IEC
- ISA/IEC 62443-2-3 — Patch Management in the IACS EnvironmentStandard · International Society of Automation / IEC
- ISA/IEC 62443-2-4 — Security Program Requirements for IACS Service ProvidersStandard · International Society of Automation / IEC
- ISA/IEC 62443-3-1 — Security Technologies for IACSBest practice · International Society of Automation / IEC
- ISA/IEC 62443-3-2 — Security Risk Assessment for System DesignStandard · International Society of Automation / IEC
- ISA/IEC 62443-4-1 — Secure Product Development Lifecycle RequirementsStandard · International Society of Automation / IEC
- ISA/IEC 62443-4-2 — Technical Security Requirements for IACS ComponentsStandard · International Society of Automation / IEC
- ISO/SAE 21434 — Road Vehicles Cybersecurity EngineeringStandard · ISO / SAE
- NERC CIP — Critical Infrastructure Protection (Bulk Electric System Cybersecurity)Regulation · North American Electric Reliability Corporation (NERC), FERC-approved
- NIST IR 7628 — Smart Grid Cybersecurity GuidelinesBest practice · NIST
- NIST SP 800-82 Rev 3 — Guide to Operational Technology (OT) SecurityBest practice · NIST
- Singapore CCoP 2.0 — Cybersecurity Code of Practice for Critical Information InfrastructureRegulation · Cyber Security Agency of Singapore (CSA)
- UNECE WP.29 R155 + R156 — Vehicle Cybersecurity + Software UpdateRegulation · UNECE
Medical & Clinical19
- 21 CFR Part 11 — Electronic Records; Electronic Signatures (FDA)Regulation · U.S. Food and Drug Administration
- DICOM — Digital Imaging and Communications in MedicineStandard · NEMA / DICOM Standards Committee
- EU Falsified Medicines Directive (2011/62/EU + Delegated Regulation 2016/161)Regulation · European Parliament and Council / European Commission
- EU GDP — Good Distribution Practice of Medicinal Products for Human Use (2013/C 343/01)Regulation · European Commission
- EU GMP — Annex 11 (Computerised Systems)Regulation · European Commission — DG SANTE
- EU GMP — EudraLex Volume 4 (Good Manufacturing Practice)Regulation · European Commission — DG SANTE
- EU GMP Annex 15 — Qualification and ValidationRegulation · European Commission (EudraLex Volume 4)
- EU MDR 2017/745 — AI-Relevant Subset for Medical-Device SoftwareRegulation · European Union (Council + Parliament)
- FDA / Health Canada / MHRA — Good Machine Learning Practice (GMLP) for Medical Device DevelopmentBest practice · FDA (US) + Health Canada + MHRA (UK)
- FDA Predetermined Change Control Plan (PCCP) for AI/ML-Enabled Device Software FunctionsBest practice · U.S. Food and Drug Administration (CDRH/CBER)
- HL7 FHIR — Fast Healthcare Interoperability ResourcesStandard · HL7 International
- ICH E6(R3) — Good Clinical Practice (GCP)Standard · International Council for Harmonisation (ICH)
- ICH Q10 — Pharmaceutical Quality SystemStandard · International Council for Harmonisation (ICH)
- ICH Q9(R1) — Quality Risk ManagementStandard · International Council for Harmonisation (ICH)
- IEC 62304 — Medical Device Software Lifecycle ProcessesStandard · IEC
- ISO 13485:2016 — Medical Devices Quality Management SystemsStandard · ISO
- ISO 14971 — Medical Device Risk ManagementStandard · ISO
- ISO 81001-1 (incl. IEC 80001-1 family) — Health software and health IT systems safety, effectiveness and securityStandard · ISO + IEC (jointly published)
- ISPE GAMP 5 — Risk-Based Approach to Compliant GxP Computerised SystemsBest practice · ISPE (International Society for Pharmaceutical Engineering)
Software Supply Chain18
- BSIMM — Building Security In Maturity Model (v15)Best practice · Black Duck (formerly Synopsys Software Integrity Group)
- CycloneDX — Bill of Materials StandardStandard · OWASP / ECMA
- DFARS Cybersecurity Clauses (252.204-7012 / -7019 / -7020 / -7021)Regulation · U.S. Department of Defense (DFARS)
- EU Cyber Resilience Act (Regulation 2024/2847)Regulation · European Union
- in-toto — Supply Chain Integrity FrameworkBest practice · CNCF / in-toto
- ISO/IEC 27036 — Information Security for Supplier RelationshipsStandard · ISO/IEC
- Microsoft Security Development Lifecycle (SDL)Best practice · Microsoft
- Microsoft SSPA — Supplier Security & Privacy AssuranceBest practice · Microsoft Corporation
- NIST SP 800-161 — Cybersecurity Supply Chain Risk Management (C-SCRM)Standard · NIST
- NIST SP 800-218 — Secure Software Development Framework (SSDF)Standard · National Institute of Standards and Technology (NIST)
- OpenSSF Scorecard — Automated OSS Project Security Health ChecksBest practice · Open Source Security Foundation (OpenSSF)
- OWASP SAMM — Software Assurance Maturity ModelBest practice · OWASP Foundation
- OWASP SCVS — Software Component Verification StandardBest practice · OWASP
- PCI Secure Software Framework (SSF)Best practice · PCI Security Standards Council
- Sigstore — Software Signing & TransparencyBest practice · OpenSSF / Sigstore
- SLSA — Supply-chain Levels for Software ArtifactsBest practice · Open Source Security Foundation (OpenSSF)
- SPDX — Software Package Data ExchangeStandard · Linux Foundation / ISO/IEC
- TUF — The Update FrameworkBest practice · CNCF / TUF
Cloud & Platform Security15
- AWS Well-Architected — Security PillarBest practice · Amazon Web Services (AWS)
- BSI C5 — Cloud Computing Compliance Criteria CatalogueBest practice · BSI (German Federal Office for Information Security)
- CIS Cloud Foundations Benchmarks (AWS / Azure / GCP)Best practice · Center for Internet Security
- CIS Docker BenchmarkBest practice · Center for Internet Security
- CIS Kubernetes BenchmarkBest practice · Center for Internet Security
- CSA Cloud Controls Matrix v4 (+ STAR)Best practice · Cloud Security Alliance
- DISA STIGs + DoD Cloud Computing SRGBest practice · U.S. Defense Information Systems Agency (DISA)
- FedRAMP — Federal Risk and Authorization Management Program (Rev 5)Regulation · FedRAMP PMO / GSA
- France ANSSI SecNumCloud — Cloud Security QualificationBest practice · ANSSI (Agence nationale de la sécurité des systèmes d'information)
- Google Cloud Architecture Framework — Security, Privacy, and Compliance PillarBest practice · Google LLC
- GovRAMP (formerly StateRAMP) — Government Risk and Authorization Management ProgramBest practice · StateRAMP Inc.
- ISO/IEC 27017:2015 — Code of Practice for Information Security Controls Based on ISO/IEC 27002 for Cloud ServicesStandard · ISO
- Microsoft Azure Well-Architected — Security PillarBest practice · Microsoft Corporation
- NSA/CISA Kubernetes Hardening GuideBest practice · NSA / CISA
- Texas TX-RAMP — Texas Risk and Authorization Management ProgramRegulation · Texas Department of Information Resources (DIR)
Financial Controls13
- Basel III — Operational Risk ManagementRegulation · Basel Committee on Banking Supervision (BIS)
- BCBS 239 — Risk Data Aggregation & Risk ReportingRegulation · Basel Committee on Banking Supervision (BIS)
- BoE PRA SS1/23 — Model Risk Management Principles for BanksRegulation · Bank of England — Prudential Regulation Authority
- EU MiCA — Markets in Crypto-Assets RegulationRegulation · European Union
- FATF 40 Recommendations (AML/CFT/CPF)Best practice · Financial Action Task Force (FATF)
- FCA AI Update — April 2024Best practice · UK Financial Conduct Authority
- FFIEC IT Examination HandbookRegulation · FFIEC
- IFRS 17 — Insurance ContractsStandard · IFRS Foundation
- NYDFS Circular Letter No. 7 (2024) — AI Systems and ECDIS in InsuranceRegulation · New York Department of Financial Services (NYDFS)
- Sarbanes-Oxley Act (SOX) — IT General Controls FocusRegulation · US Congress
- SOC 1 (SSAE 18 / ISAE 3402) — Controls Relevant to Financial ReportingBest practice · AICPA (SSAE 18) / IAASB (ISAE 3402)
- Solvency II — EU Insurance Prudential RegimeRegulation · European Union (EIOPA)
- SR 11-7 — Model Risk ManagementRegulation · Federal Reserve / OCC
Sustainability & ESG13
- AWS Well-Architected — Sustainability PillarBest practice · Amazon Web Services (AWS)
- CDP — Environmental Disclosure and ScoringBest practice · CDP (formerly Carbon Disclosure Project)
- CSRD / ESRS — EU Corporate Sustainability ReportingRegulation · European Union (EFRAG develops ESRS)
- GHG Protocol — Corporate Accounting and Reporting StandardBest practice · World Resources Institute (WRI) and World Business Council for Sustainable Development (WBCSD)
- Google Cloud Architecture Framework — Sustainability PillarBest practice · Google LLC
- Green Software Foundation — Principles + Software Carbon IntensityBest practice · Green Software Foundation
- GRI Standards — Global Reporting InitiativeBest practice · Global Reporting Initiative (GRI)
- ISO 14001 — Environmental Management SystemStandard · ISO
- ISO 14064 — Greenhouse Gas Accounting, Quantification and VerificationStandard · ISO
- ISO 50001:2018 — Energy Management SystemsStandard · ISO
- ISSB IFRS S1 + IFRS S2 — Sustainability + Climate DisclosureStandard · IFRS Foundation / ISSB
- SBTi — Science Based Targets initiativeBest practice · Science Based Targets initiative (SBTi)
- TCFD — Task Force on Climate-related Financial DisclosuresBest practice · Task Force on Climate-related Financial Disclosures (Financial Stability Board)
Functional Safety12
- ANSI/ISA TR84.00.07 — Guidance on the Evaluation of Fire, Combustible Gas, and Toxic Gas System EffectivenessBest practice · International Society of Automation
- ANSI/ISA-84.00.01 (IEC 61511) — Functional Safety: Safety Instrumented Systems for the Process IndustryStandard · International Society of Automation / IEC
- ARP 4754A — Guidelines for Development of Civil Aircraft and SystemsStandard · SAE International
- ARP 4761A — Guidelines and Methods for Conducting the Safety Assessment Process on Civil Airborne Systems and EquipmentStandard · SAE International
- DO-178C — Software Considerations in Airborne Systems and Equipment CertificationStandard · RTCA / EUROCAE
- DO-254 / ED-80 — Design Assurance Guidance for Airborne Electronic HardwareStandard · RTCA / EUROCAE
- EN 50128 — Railway Software SafetyStandard · CENELEC
- IEC 61508 — Functional Safety of E/E/PE Safety-Related SystemsStandard · IEC
- IEC 61882 — Hazard and Operability Studies (HAZOP)Standard · IEC (International Electrotechnical Commission)
- IEC 62278 (EN 50126) — Railway RAMSStandard · IEC / CENELEC
- ISO 26262 — Road vehicles — Functional safetyStandard · ISO
- MIL-STD-882E — DoD Standard Practice for System SafetyStandard · U.S. Department of Defense
Operational Resilience10
- APRA CPS 230 — Operational Risk ManagementRegulation · Australian Prudential Regulation Authority (APRA)
- AWS Well-Architected — Reliability PillarBest practice · Amazon Web Services (AWS)
- Basel — Principles for Operational Resilience (BCBS)Best practice · Basel Committee on Banking Supervision (BCBS/BIS)
- BCI Good Practice Guidelines — Business ContinuityBest practice · Business Continuity Institute (BCI)
- DORA — Digital Operational Resilience Act (EU 2022/2554)Regulation · European Union
- Google Cloud Architecture Framework — Reliability PillarBest practice · Google LLC
- ISO 22301 — Business Continuity Management SystemStandard · ISO
- Microsoft Azure Well-Architected — Reliability PillarBest practice · Microsoft Corporation
- NIST SP 800-34 — Contingency Planning Guide for Federal Information SystemsStandard · National Institute of Standards and Technology (NIST)
- UK Operational Resilience (FCA PS21/3 + PRA SS1/21)Regulation · UK FCA + PRA + Bank of England
Identity & Trust10
- API Authorisation Hardening — OAuth 2.0 Security BCP + OpenID FAPI 2.0Best practice · IETF / OpenID Foundation
- eIDAS 2.0 — European Digital Identity FrameworkRegulation · European Union
- ENISA Post-Quantum Cryptography — Guidance and TransitionBest practice · ENISA (European Union Agency for Cybersecurity)
- FIDO2 / WebAuthn — Phishing-Resistant AuthenticationStandard · W3C / FIDO Alliance
- FIPS 140-3 — Security Requirements for Cryptographic ModulesStandard · NIST
- NIST IR 8547 — Transition to Post-Quantum Cryptography StandardsStandard · NIST
- NIST Post-Quantum Cryptography (FIPS 203/204/205)Standard · NIST
- NIST SP 800-63-4 — Digital Identity GuidelinesBest practice · NIST
- NSA CNSA 2.0 — Commercial National Security Algorithm Suite 2.0Regulation · U.S. National Security Agency (NSA)
- PSD2 + SCA RTS (EU Payment Services Directive + Strong Customer Authentication)Regulation · European Union
Governance, Risk & Compliance10
- COBIT 2019 — Governance and Management Framework for Enterprise Information and TechnologyBest practice · ISACA
- COSO ERM — Enterprise Risk Management (Integrating with Strategy and Performance)Best practice · COSO (Committee of Sponsoring Organizations of the Treadway Commission)
- ISO 31000 — Risk Management GuidelinesStandard · ISO
- ISO/IEC 31010 — Risk Assessment TechniquesStandard · ISO/IEC
- ISO/IEC 38500 — Governance of IT for the OrganizationStandard · ISO/IEC
- ISO/TC 307 — Blockchain & Distributed Ledger TechnologiesStandard · ISO/IEC
- NISPOM / 32 CFR Part 117 — National Industrial Security Program Operating ManualRegulation · U.S. DoD / Defense Counterintelligence and Security Agency (DCSA)
- NIST SP 800-37 Rev 2 — Risk Management Framework (RMF)Best practice · NIST
- SOC 2 — Trust Services Criteria (2017 with 2022 revisions)Best practice · AICPA
- US Export Control — ITAR + EARRegulation · U.S. Department of State (DDTC) + Department of Commerce (BIS)
Data Governance9
- ACORD Data StandardsBest practice · ACORD
- CDMC — Cloud Data Management Capabilities (v1.1)Best practice · Enterprise Data Management Council (with Google Cloud sponsorship)
- DAMA-DMBOK: Data Management Body of Knowledge (2nd Edition)Best practice · DAMA International (Technics Publications)
- DCAM — Data Capability Assessment Model (EDM Council)Best practice · Enterprise Data Management Council
- EU Data Act (Regulation 2023/2854)Regulation · European Union
- GS1 EPCIS 2.0 + Core Business Vocabulary — Supply-Chain Visibility Event StandardStandard · GS1 AISBL
- ISO 15489 — Records ManagementStandard · ISO
- ISO 19650 — BIM / Built-Asset Information ManagementStandard · ISO
- ISO/IEC 5259 — Data Quality for Analytics and Machine LearningStandard · ISO/IEC
Software Architecture7
- arc42 — Open Architecture Documentation TemplateBest practice · arc42 community (Gernot Starke, Peter Hruschka)
- Architecture Decision Records (ADR Pattern)Best practice · Open methodology (Michael Nygard, ThoughtWorks community)
- AUTOSAR — AUTomotive Open System ARchitectureBest practice · AUTOSAR Partnership (consortium)
- C4 Model — Software Architecture DiagrammingBest practice · Simon Brown (author)
- ISO/IEC/IEEE 42010 — Architecture DescriptionStandard · ISO/IEC/IEEE joint publication
- Kruchten 4+1 View Model of Software ArchitectureBest practice · Philippe Kruchten / IEEE Software (Nov 1995)
- TOGAF — The Open Group Architecture FrameworkBest practice · The Open Group
Industrial Automation7
- ANSI/ISA-100.11a — Wireless Systems for Industrial AutomationStandard · International Society of Automation
- ANSI/ISA-101.01 — Human Machine Interfaces for Process Automation SystemsStandard · International Society of Automation
- ANSI/ISA-18.2 — Management of Alarm Systems for the Process IndustriesStandard · International Society of Automation
- ANSI/ISA-88 (IEC 61512) — Batch ControlStandard · International Society of Automation / IEC
- ANSI/ISA-95 (IEC 62264) — Enterprise-Control System IntegrationStandard · International Society of Automation / IEC
- IEC 61850 — Power Utility Automation CommunicationStandard · IEC
- IEEE 1547 — Interconnection of Distributed Energy ResourcesStandard · IEEE
AI Security5
- Google SAIF — Secure AI FrameworkBest practice · Google
- MITRE ATLAS — Adversarial Threat Landscape for AIBest practice · MITRE
- NIST AI 100-2 — Adversarial ML TaxonomyStandard · NIST
- OWASP Machine Learning Security Top 10Best practice · OWASP
- OWASP Top 10 for LLM ApplicationsBest practice · OWASP
Accessibility5
- ADA Title III — Public Accommodations (Digital Accessibility)Regulation · US DOJ
- EN 301 549 — ICT Accessibility Requirements (EU)Standard · ETSI / CEN / CENELEC
- Section 508 — ICT Accessibility (Revised 508 Standards)Regulation · US Access Board
- WAI-ARIA Authoring Practices Guide (APG)Best practice · W3C WAI
- WCAG 2.2 — Web Content Accessibility GuidelinesBest practice · W3C — World Wide Web Consortium
Quality Management3
- AS9100D:2016 — Quality Management Systems for Aviation, Space, Defense OrganizationsStandard · SAE International / IAQG
- IATF 16949:2016 — Automotive Quality Management SystemStandard · International Automotive Task Force (IATF)
- ISO 9001:2015 — Quality Management SystemsStandard · ISO
Trademarks and attribution
Framework names are the property of their publishers and are used here to identify the frameworks. cajeX is not affiliated with or endorsed by them. ACORD is a registered trademark of ACORD Corporation. ARP 4761A is a publication of SAE International. ATT&CK® and D3FEND™ are trademarks of The MITRE Corporation. AUTOSAR® is a registered trademark of the AUTOSAR partnership. Automotive SPICE® is a registered trademark of the Verband der Automobilindustrie (VDA). BCI® and the Good Practice Guidelines are trademarks of the Business Continuity Institute. Based on Chinese national standards (GB/T) published by TC260/SAC; clause text is paraphrased. CDMC® is a registered trademark of the EDM Council. CMMI is a registered trademark of ISACA. COBIT® is a registered trademark of ISACA. COSO® is a registered trademark of the Committee of Sponsoring Organizations of the Treadway Commission. CVSS is a trademark of FIRST.org, Inc. DAMA-DMBOK® is a registered trademark of DAMA International. Methodology summaries here are paraphrased educational references; consult the 2nd Edition (Technics Publications, 2017) for binding text. DCAM® is a registered trademark of the EDM Council. DO-254 / ED-80 are publications of RTCA, Inc. and EUROCAE. DO-326A / ED-202A and the DO-356A / DO-355 / DO-379 family are publications of RTCA, Inc. and EUROCAE. EN standards are published by CEN-CENELEC; all rights reserved. GAMP is a registered trademark of ISPE. GRI® is a registered trademark of the Global Reporting Initiative. GS1, EPCIS, EPC and GS1 Digital Link are trademarks of GS1 AISBL. Clause bodies are cajeX paraphrases; consult the GS1 standards for binding text. GSMA NESAS is a trademark of the GSM Association. 3GPP is a registered trademark of ETSI. HITRUST CSF® is a registered trademark of HITRUST Alliance. IACS Unified Requirements are published by the International Association of Classification Societies. IATF 16949 is published by the International Automotive Task Force. IEC is a registered trademark of the International Electrotechnical Commission. IEC standards are copyright IEC. Clause text is paraphrased; titles derive from the public table of contents. IEEE is a registered trademark of the Institute of Electrical and Electronics Engineers, Inc. IFRS is a registered trademark of the IFRS Foundation. ISA® is a registered trademark of the International Society of Automation. ISMS-P is a certification scheme of the Korea Internet & Security Agency (KISA). ISO and IEC are registered trademarks of the International Organization for Standardization + International Electrotechnical Commission. ISO and IEC are registered trademarks of the International Organization for Standardization and the International Electrotechnical Commission. ISO and IEC are registered trademarks of their respective organizations. ISO and IEC standards are copyright ISO/IEC. Clause text is paraphrased; titles derive from the public table of contents. ISO and SAE are registered trademarks of their respective organizations. ISO is a registered trademark of the International Organization for Standardization. ISO standards are copyright ISO. Clause text is paraphrased; titles derive from the public table of contents. ISO, IEC and IEEE are registered trademarks of their respective organizations. ISTQB is a registered trademark of the International Software Testing Qualifications Board. IT-Grundschutz is a publication of the German Federal Office for Information Security (BSI). IT4IT® is a registered trademark of The Open Group. ITIL® is a registered trademark of PeopleCert. International Electrotechnical Commission retains all trademarks and copyrights in the source standard. Microsoft, SSPA, and the Data Protection Requirements are trademarks/property of Microsoft Corporation. NEN 7510 is a publication of the Royal Netherlands Standardization Institute (NEN). OWASP® is a registered trademark of the OWASP Foundation. PCI DSS® is a registered trademark of the PCI Security Standards Council, LLC. PCI Security Standards Council is a registered trademark of PCI Security Standards Council, LLC. PMBOK and PMI are registered trademarks of the Project Management Institute, Inc. PRINCE2 is a registered trademark of PeopleCert. RTCA documents are published by RTCA, Inc. SAE is a registered trademark of SAE International. SAFe and Scaled Agile Framework are registered trademarks of Scaled Agile, Inc. SOC 1 and the SSAE standards are publications of the AICPA. SOC 2® is a registered service mark of the American Institute of Certified Public Accountants (AICPA). STIX, TAXII are trademarks of OASIS Open. SWIFT is a registered trademark of S.W.I.F.T. SCRL. TISAX and VDA ISA are registered trademarks of the ENX Association / VDA. TOGAF is a registered trademark of The Open Group. The GHG Protocol is a trademark of WRI and WBCSD. W3C® and WCAG are trademarks of the W3C.